Trusted with your operation, not just told to be.
You're putting your fleet, your crew records, and your clients' information into this system. That's not a small thing to ask. Here's exactly what protects it.
You're not just trusting software. You're trusting a system with judgment.
Who can see what. Whether a record can be quietly changed. Whether the aircraft someone's adding to your fleet actually belongs to them. This page is about how we take that seriously.
Specific measures, not a promise to try our best.
Verified Fleet, Not Self-Declared
Every aircraft linked to your account is confirmed against real aviation records before it's associated with you - so no one can add an aircraft they don't actually operate.
Staff Access Is Scoped And Timed
When our support staff need to look into your ticket, that access is tied to the specific ticket, expires automatically, and is fully logged - not standing access to your account.
A Record Nobody Can Quietly Edit
Every account and data change is logged in a record that can't be updated or deleted afterward - not by us, not by anyone, at any layer.
Your Data Stays Yours
Strict separation between operators - another company on the platform can never see your data, even by accident, even through a shared feature.
Access Matches The Role, Not Everyone Sees Everything
Executives, HR, and operational staff each see what their role actually needs - not a single shared login with every permission switched on.
Enterprise Sign-In When You Need It
Real SAML SSO for teams whose own security policy already dictates how sign-in has to work.
Everyone sees what their job needs. Nothing more.
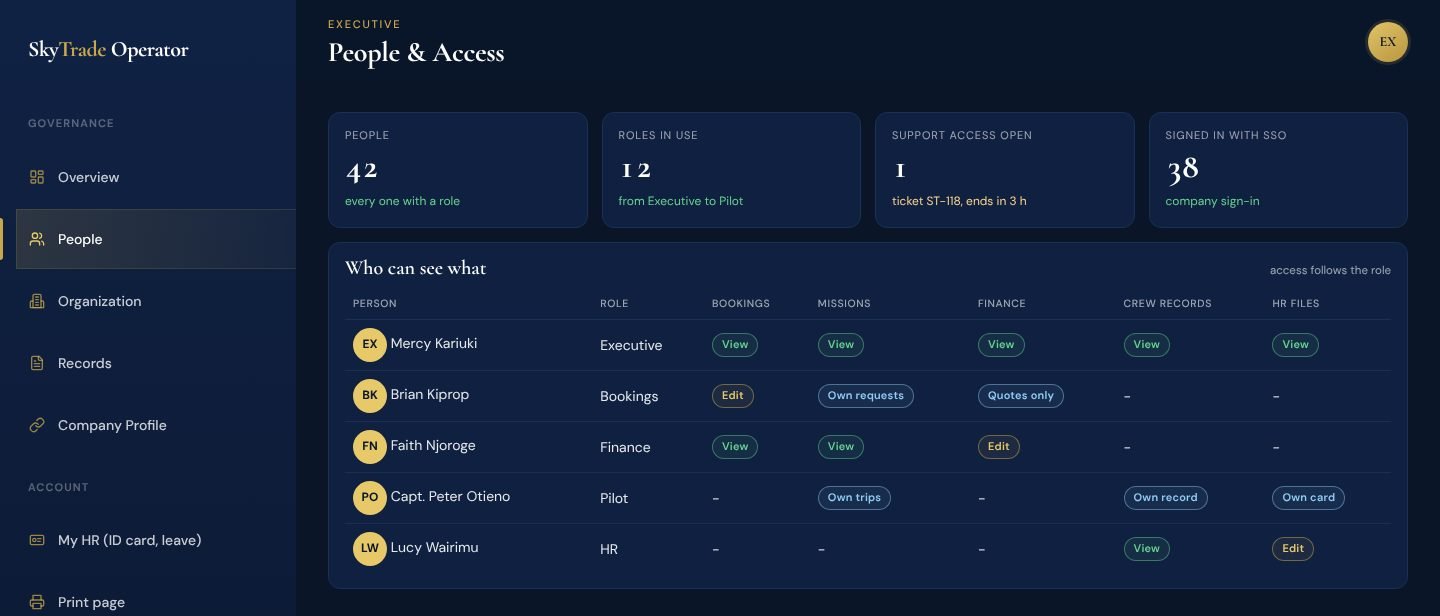
Each person signs in with their own account and one of 12 roles. The role decides what they can see and what they can change - a pilot sees their own trips and record, Finance edits invoices, HR edits staff files.
- Regional executives see their own region; only the HQ Executive sees every region.
- HR decides which details each person may update on their own ID card.
- Company sign-in (SSO) for teams whose policy requires it.
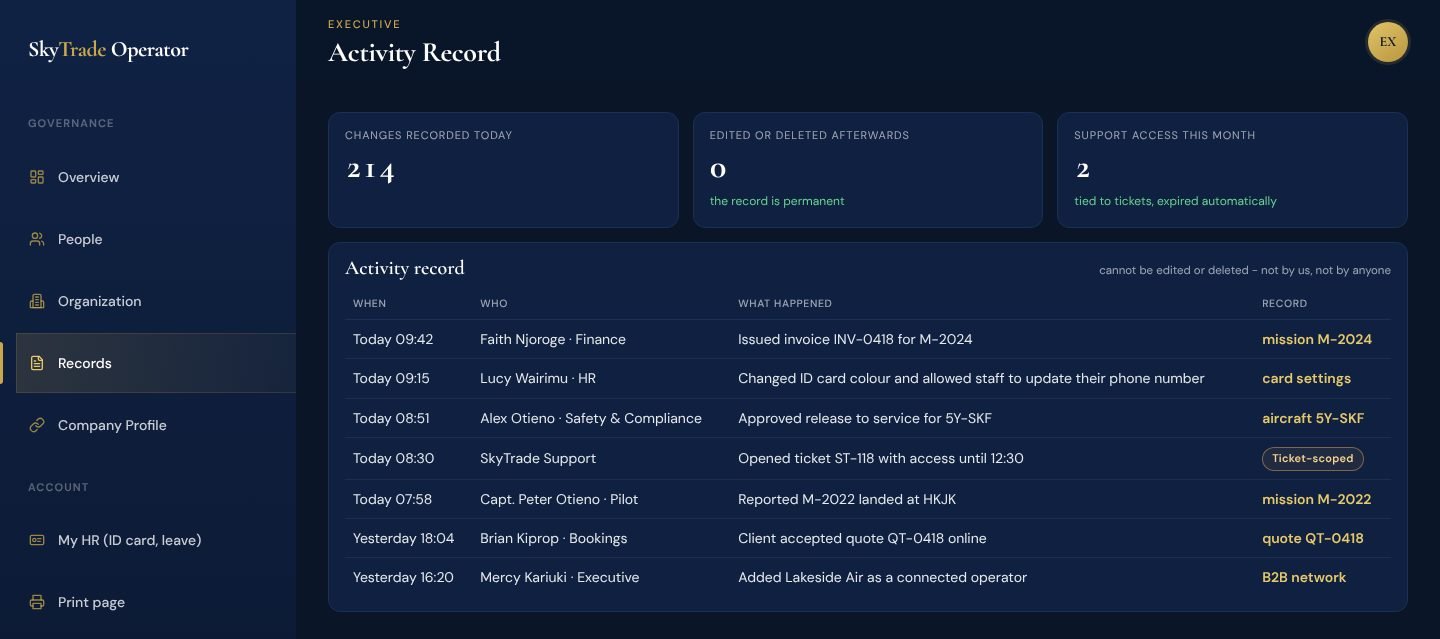
Every change, who made it, and when - permanently.
Invoices issued, aircraft released to service, card settings changed, partners connected: each action is written to an activity record that cannot be edited or deleted afterwards.
- Support access is tied to a ticket, ends automatically and appears in the record.
- Every entry links to its record - the mission, aircraft or quote it changed.
Not an open marketplace. Verified operators, with a verified fleet.
Every operator is reviewed before approval, and every aircraft added to a fleet is confirmed against real aviation records first. When you connect with another operator or borrow their aircraft, you're dealing with someone who's actually been checked - not an anonymous listing.
A real Data Processing Addendum, on request.
If your security team needs formal documentation before you can move forward, we have it - not a promise to get back to them once you're already a customer.